

Free Download
AI Policy Template
The AI policy built to be used, not just filed away...
 Policy · v1.0
Use Policy
AI is already part of how your team works, whether there's a policy for it or not 😬
Without one, you've no real way of knowing what's being shared, which tools people are actually using, or whether any of that is putting confidential or personal data at risk...
So we've written the policy for you: permitted tools, staff obligations, data protection, the lot 🙌
What's in this template?
If someone on your team has ever pasted a paragraph into ChatGPT to tidy it up, congratulations, you're already using AI at work. Whether that's fine or a problem depends entirely on whether there's a policy for it.
Most scaleups don't have one yet. Then an investor, an enterprise customer, or a due diligence questionnaire asks for it, and there's a scramble.
This template skips the scramble. It's the real thing, not a teaser: a full AI acceptable use policy, ready to copy, edit and roll out to your team today.
📄 What's inside the AI policy template
It's a full AI acceptable use policy, built section by section around the decisions your business actually needs to make about AI.
Why bother with an AI policy now
AI regulation is moving fast. Enforcement is catching up.
The EU AI Act's rules on general-purpose AI have applied since August 2025. The higher-risk use cases, think hiring, credit scoring, biometrics, follow between December 2027 and August 2028. You can track the detail on the European Commission's AI Act page.
The UK hasn't passed a single, cross-sector AI law yet. But the ICO has been clear that UK GDPR already applies in full to AI. Any tool that touches personal data needs a lawful basis, and often a DPIA, before it goes anywhere near day-to-day work.
None of this is theoretical. Investors and enterprise customers now routinely ask about AI use during due diligence and procurement reviews. "We don't have a policy yet" isn't the answer anyone wants to give at that point.
Who this AI policy template is built for
This one's for scaleups, not enterprises. It's a good fit if your business:
- Has roughly 50 to 250 employees
- Processes personal data at scale, or handles special category data (health, biometric, financial)
- Has a multinational customer base, or employees across multiple countries
- Needs to prove compliance to investors, enterprise customers or regulators, without a full in-house legal or privacy team
Trust Keith works with data-centric scaleups across fintech, healthtech, HR tech and ed tech, exactly the kind of businesses where "we'll sort an AI policy eventually" isn't really a plan. Take a look at how Trust Keith supports AI governance as a business grows.
Got questions on where your business stands?
Trust Keith runs free monthly Office Hours where you can ask a privacy expert directly.
How to use this AI policy template
Find and replace every instance of {Company Name} throughout the document.
Assign a Senior Owner, or a Risk Committee, responsible for approving new AI tools and reviewing risk.
Add every approved tool to your information asset register, alongside the supplier checks you've already run on it.
A policy nobody's read isn't a policy, it's a PDF. Fold AI into your regular staff training so people know the rules before they paste something they shouldn't into a chatbot.
Have a privacy expert check it's proportionate and accurate before you rely on it. Trust Keith customers get expert-tailored, audit-ready policies as standard; going it alone just means budgeting time for a proper review.
Where most AI policies go wrong
A copy-pasted AI policy nobody's tailored to your actual tools and risk won't hold up under real scrutiny.
Without one, people pick their own AI tools, and you lose all visibility over what's happening to your data. This has a name: shadow AI.
AI tools and regulation change fast. A policy nobody revisits goes stale within months.
If your AI tool touches personal data, UK GDPR expects a Data Protection Impact Assessment, not just a policy in a drawer.
Anyone with access to your systems needs to play by the same rules as employees.
Most AI policy failures aren't malicious. They're just people who never knew the rules existed.
Frequently asked questions
What should an AI policy include?
Who it applies to, which AI tools are permitted (and how new ones get approved), security and confidentiality rules, staff obligations, the business's own obligations like monitoring and DPIAs, and plain-English definitions. Trust Keith's free template covers all of it.
Do UK businesses legally need an AI policy?
There's no single UK law that says every business must have a named AI policy document. But if a business uses AI tools that process personal data, UK GDPR and the Data Protection Act 2018 already apply in full, and the ICO expects businesses to show how that risk is being managed. An AI policy is the practical way most do it.
Is this AI policy template really free?
Yes. Trust Keith built this to help data-centric scaleups get a policy in place quickly. It's free and it's yours to edit, use and share internally.
Does this template cover the EU AI Act?
It covers the acceptable use, security and governance basics that apply regardless of jurisdiction, and it's built with UK and EU AI regulation in mind. Businesses operating in the EU, or serving EU customers, should get it reviewed against the EU AI Act's current requirements, since high-risk provisions are being phased in through 2027 and 2028.
How often should an AI policy be updated?
At least once a year, and whenever a new AI tool is introduced, the business expands into a new market, or a relevant law changes. Trust Keith customers review theirs every quarter as part of their risk cycle.
Does this template replace legal advice?
No. It's a strong starting point, but it should be reviewed by a privacy expert before being relied on, especially for businesses processing special category data or operating across multiple jurisdictions.
What's the difference between an AI policy and an AI governance framework?
An AI policy sets the day-to-day rules for how staff use AI tools safely and compliantly. An AI governance framework is broader: how a business assesses, approves and monitors AI use strategically, often with risk committees and board reporting. This template gives you the policy layer, with a Risk Committee already built in, so it's easy to grow into a fuller framework later.
Disclaimer: This template is provided free of charge for general information purposes only. It does not constitute legal advice and should not be relied upon as such.
Everything you need to run privacy properly in any jurisdiction
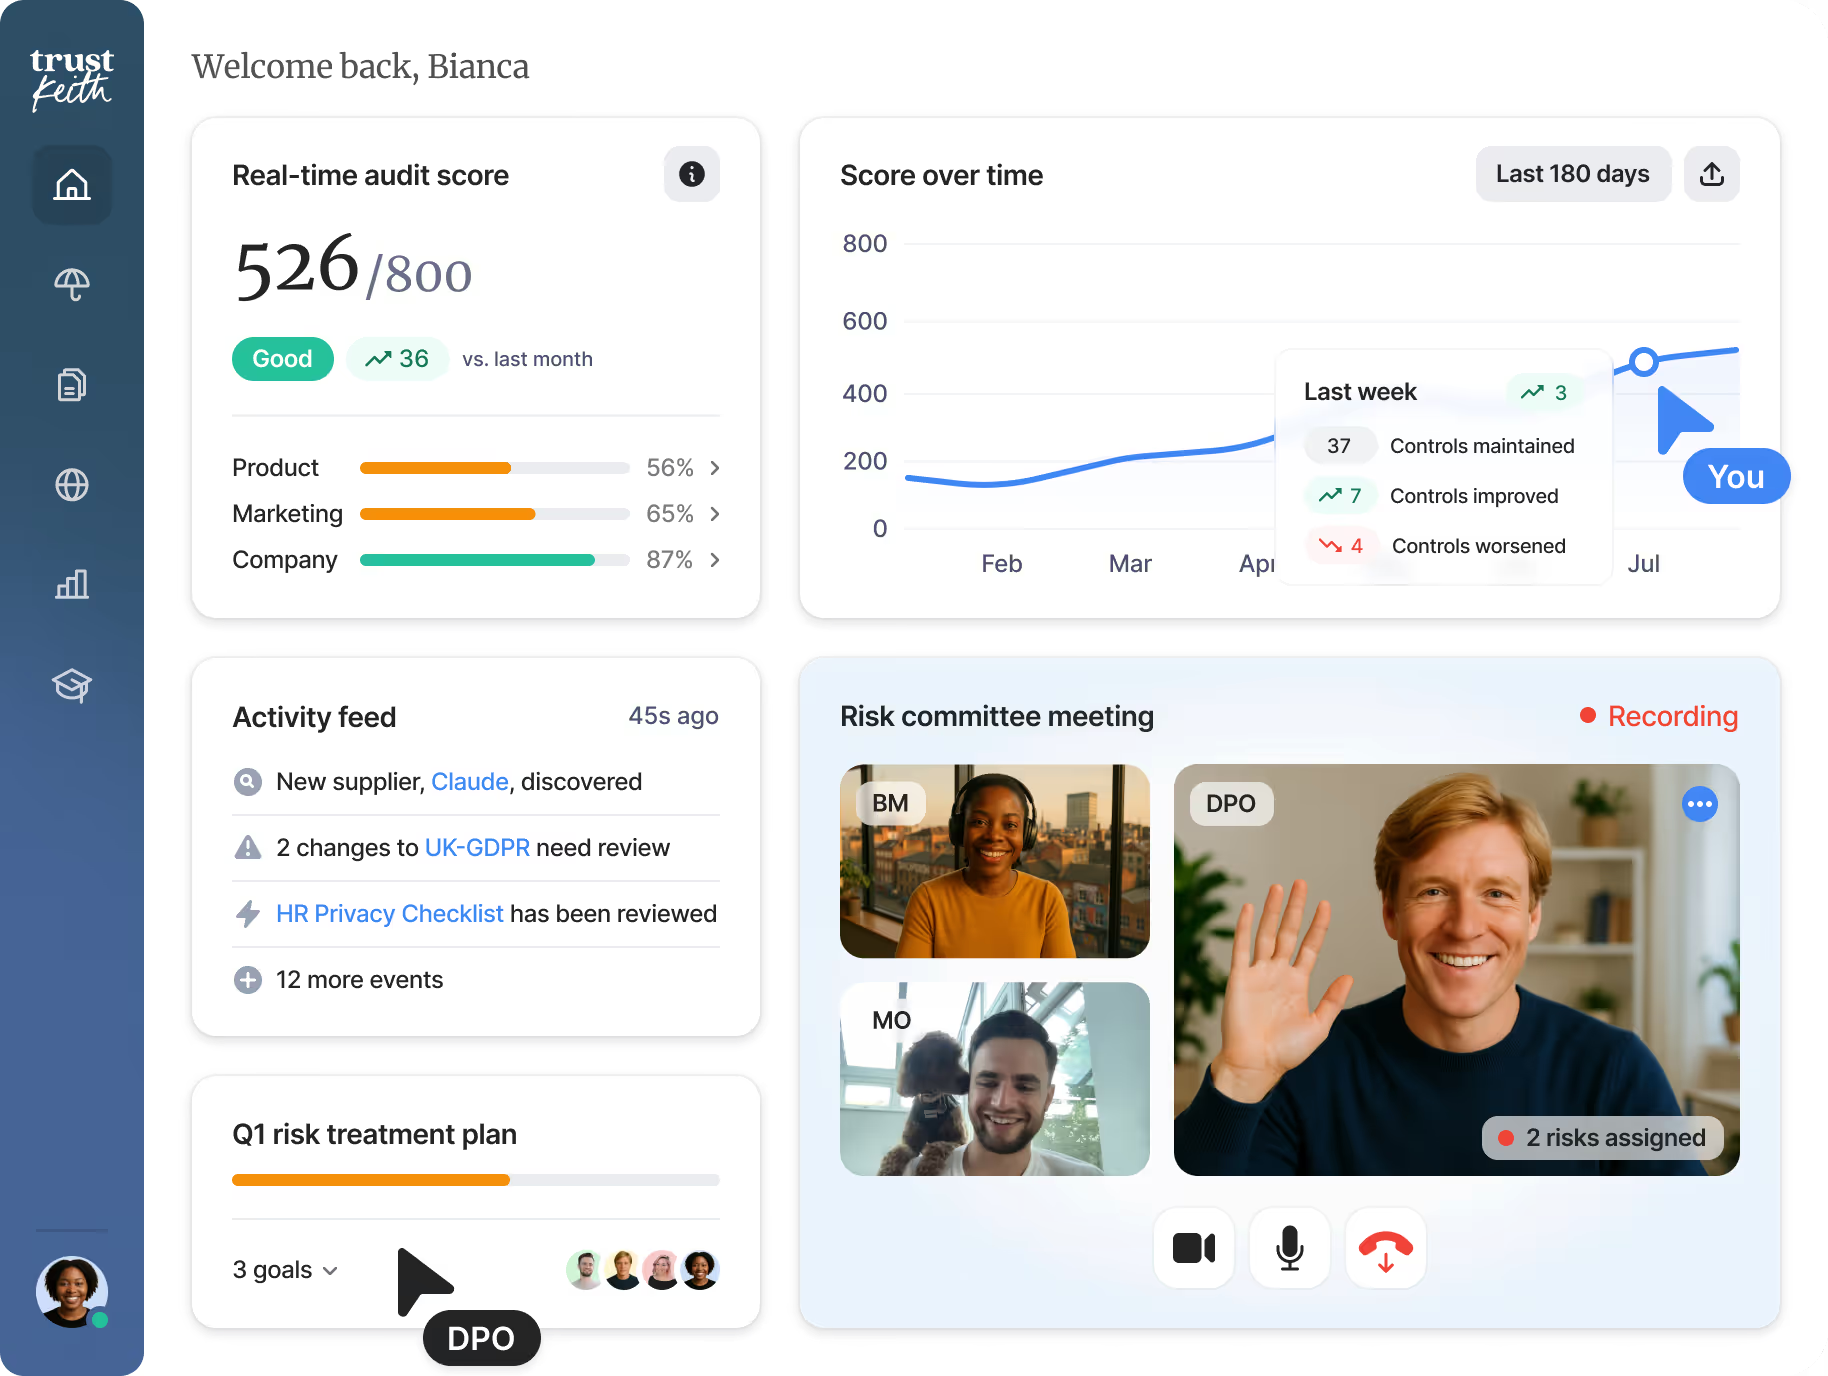
Trust Keith holds your hand to get you (and keep you!) as compliant as you need by giving you access to a dedicated human expert and an intelligent platform.
Find out more →